Rejected over privacy? Let's get you resubmitted.
Review sent your build back over data collection, account deletion or a privacy answer that doesn't match your app. I fix the app so the answers are true, and write the reply you send back.
Book the $1,200 rejection fixIf your rejection isn't mine to fix, I say so on the free call and you pay nothing.
I reply within 24 hours. Paid up front once you've said yes, before I start.
I'm Nate Parker, a senior software engineer. Proving what happens to personal data is a large part of my day job, on a healthcare platform.
The rejections I can fix
These are the ones AI-built apps hit again and again.
- You collect data you didn't declareYour privacy answers say one thing and the app does another, usually because something you added is sending data you never knew about.
- No way to delete an account in the appIf people can sign up inside the app, Apple requires they can delete the account there too.
- The encryption question answered wrongAlmost every app gets this one wrong at least once. It's a small fix and a common bounce.
- Google's data safety form doesn't matchPlay compares the form against what your app actually sends. A wrong answer there can pull the listing, not just block the update.
- Keys or test code left in the buildReviewers find them. So does anyone who downloads your app and opens it up.
What I do once you book
- Tell you what they actually wantReview writes vaguely on purpose. I read the rejection against the real rule and tell you what has to change.
- Fix the app, not just the paperworkWhere your app really does collect the data, I change the app, so the answer you give is true.
- Fill in the privacy answers with youEvery answer matched to what your app does, so the next build doesn't bounce for the same reason.
- Write the reply to reviewThe note that goes back with your resubmission, saying what changed.
Rejection fix, $1,200 flat fee
Book the $1,200 rejection fixHow it goes
- Send me the rejectionPaste what App Store Connect or Play Console sent you. I reply within 24 hours, usually much sooner.
- We talk for 15 minutes, freeI tell you honestly whether this is mine to fix. Some rejections are about design or screenshots. Those aren't my job and I'll say so.
- I fix it and you resubmitUsually within three business days. After that it's their review queue, which nobody controls.
Introductory price for my first ten clients. Goes up after that.
One app, one rejection. If the next build bounces again for something I was hired to fix, I fix that too at no charge.
- The rejection explained in plain English
- Fixes to the app itself, not just the form
- Privacy answers and data safety form filled in with you
- The reply to send back with your resubmission
- Two weeks of follow-up questions
If your rejection isn't mine to fix, I say so on the free call and you pay nothing.
I reply within 24 hours. Paid up front once you've said yes, before I start.
Why it's $1,200
Flat, and it covers the whole thing: reading the rejection, fixing the app, writing the privacy answers, drafting the reply. The alternative is guessing by the hour.
Figures from freelance security consultant rates. Not my former prices: I have never charged them.
Who you're hiring
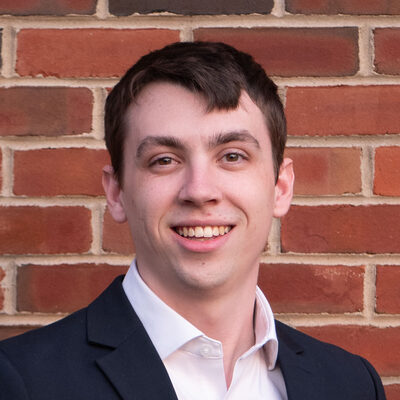
For five years I've built and defended the platform at a healthcare software company, where security is a large part of my job. I'm also the security engineer for a B2B software startup, and I've found real vulnerabilities in widely used open-source code. I've built, shipped and sold my own software too, so I know what it's like when the app is your income. You work with me directly.
Across my professional security work, not App Locksmith alone. The clients are under NDA, so no names, ever — including yours.